Cybersecurity Awareness Month is a good time to remind people about phishing, passwords and MFA. For MSPs, there's a second question worth asking: are the controls behind all of that actually doing what you think they are?
Every October, businesses remind users to spot suspicious emails, use strong authentication and think before they click. That matters, but it only covers the people side.
A tenant can have MFA enabled and Conditional Access policies configured, look well protected, and still have at least one way in that no policy blocks.
Configured does not mean enforced.
Checking Conditional Access by hand is possible. Checking it properly, across every combination of users, applications, devices, locations and authentication paths, is a much bigger job.
Multiply that across an MSP customer base and it becomes the kind of security work that keeps slipping down the list, simply because there aren't enough hours in the day.
So for Cybersecurity Awareness Month, we wanted to give MSPs something practical.
Cybersecurity Awareness Month offer
During October, we're giving MSPs longer to put Overe Conditional Access Assurance to the test. Start now and use the full Overe platform free until 31 October. Our standard trial is only 14 days.
The extra time means you can connect a tenant, run CAA, investigate anything it finds and see how the wider Overe platform fits into your Microsoft 365 security operations.
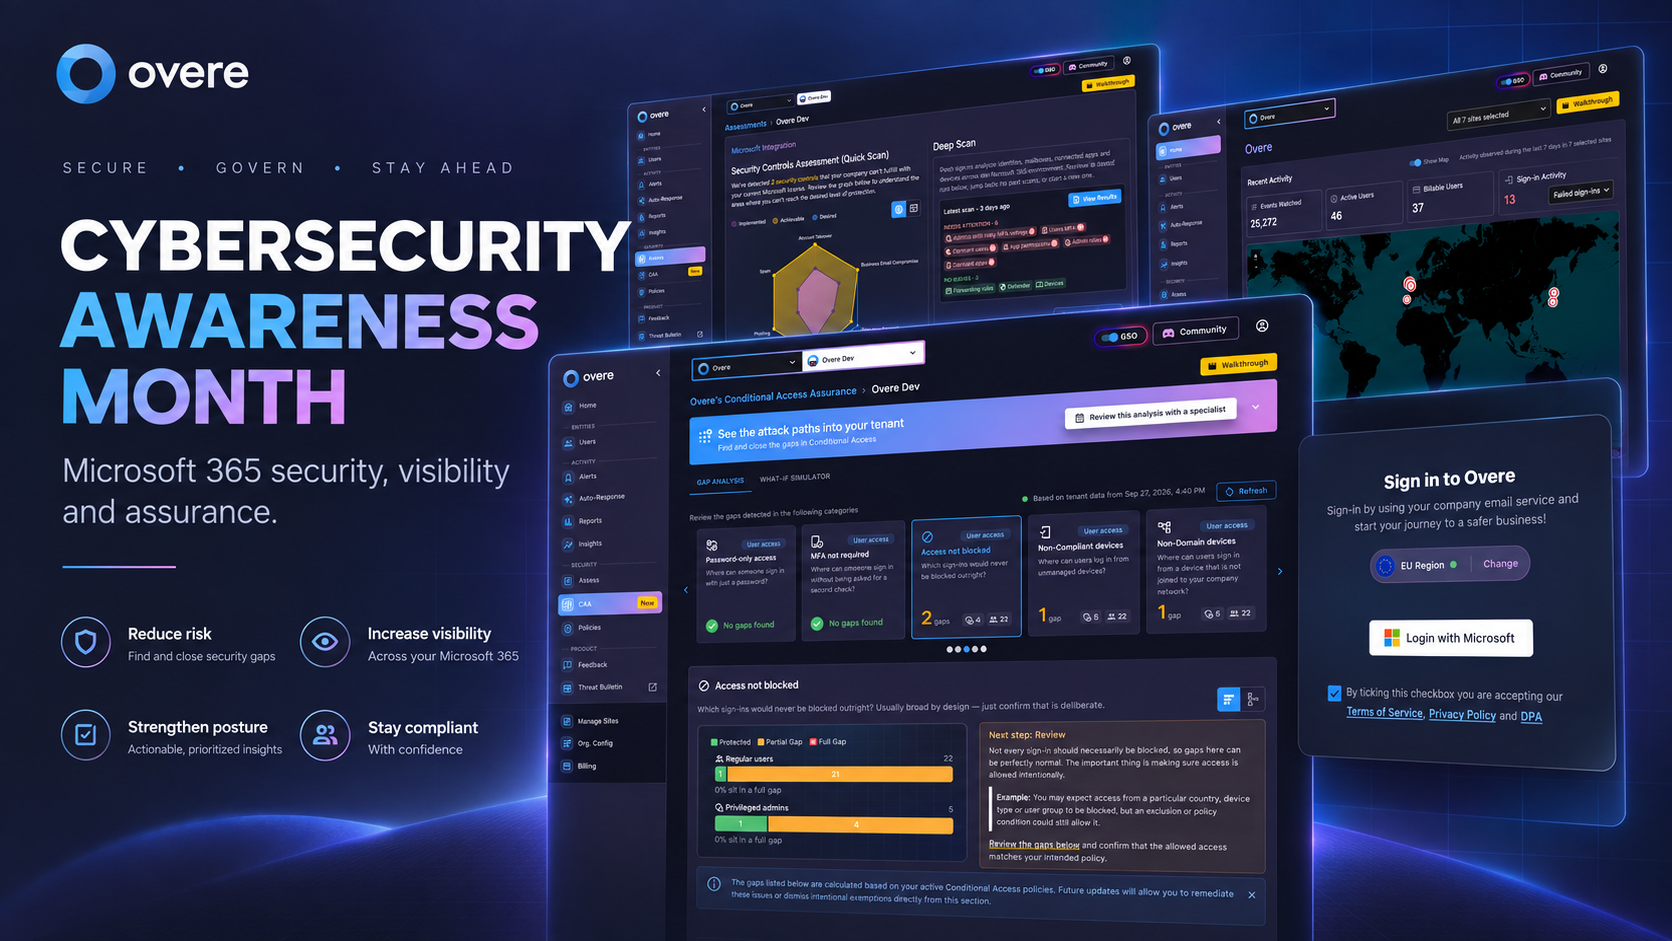
Once a tenant is connected, CAA analyses the access paths through its Conditional Access configuration and shows where access is protected, conditionally protected, or where gaps exist. Rather than reading policies one by one, you can drill straight into the users, apps and conditions creating the exposure.
This isn't really about extending a software trial. We want MSPs to have an easy reason to start a security conversation with their customers.
Instead of opening with "We should probably review your Conditional Access policies," you can walk in with evidence:
"We tested how access to Microsoft 365 is actually being enforced. Here's what we found."
The result might be something that needs fixing, confirmation that existing controls are doing their job, or simply more confidence for the customer in their Microsoft 365 environment. Either way, you get there without hours of manual policy review.
Kevin at Electron IT, a UK MSP using Overe, put it this way:
"The biggest difference is confidence. We know our customers' Microsoft 365 environments are being monitored consistently, and we're spending far less time on repetitive administration."
Keep training users, talking about phishing and pushing MFA. But this October, take a few minutes to check whether the technology behind those controls is actually protecting every path you expect it to.
Test one Microsoft 365 tenant. See how access is actually being enforced. Use Overe free until 31 October.